TL;DR
- Base64 encoding is not encryption: Kubernetes Secrets are base64 encoded, not encrypted, so committing one to a Helm chart puts a working credential in Git.
- Encrypt in the chart or sync at deploy time: Encrypt values inside the chart with helm-secrets and SOPS or Sealed Secrets, or keep values out of the chart and sync them at deploy time with External Secrets Operator or Vault Secrets Operator.
- External Secrets Operator as the default pick: External Secrets Operator needs nothing installed where Helm runs, so Argo CD, Flux, and GitHub Actions work unchanged, which makes it the default choice.
- SOPS with age instead of PGP keys: Use age encryption instead of PGP keys with SOPS. It gives comparable protection for encrypting a values file, with far simpler key management.
- Reloader for pods after secret rotation: Rotating a secret does not restart your pods, a gap most guides miss. Add Reloader and the auto annotation to close the gap.
If you have ever pasted a database password into values.yaml and then paused for a second before running git commit, this one is for you. A Helm chart is built to be shared. A password is built to be shared with nobody. This guide walks through the four ways teams reconcile those two facts, with a working example for each, plus the rotation gap that tends to show up months later.
The two ways to keep secrets out of your charts
Every approach in this guide is a variation on one of two ideas, and after years of doing this I have yet to find a third:
- Store encrypted secrets in the chart. Encrypt the values before they touch Git, then decrypt them at deploy time. The chart stays self-contained and safe to commit. Storing secrets this way means you own the encryption keys and their distribution.
- Keep the secret values out of the chart entirely. The chart holds only a reference, and the real value is fetched from a secret manager when the app deploys. Nothing sensitive is ever stored in Git. You take on a runtime dependency in exchange.
helm-secrets and Sealed Secrets are the first idea. External Secrets Operator and Vault Secrets Operator are the second.
Option one: Encrypt chart values with helm-secrets and SOPS
The helm-secrets plugin is a widely used option for Helm secrets management, and it covers both approaches: it can encrypt Helm values inside the chart, or fetch them from a cloud secret manager at install time.
How the helm-secrets plugin works
What is a Helm plugin, then? Helm plugins are extensions that add commands to the Helm CLI. You install one with helm plugin install, then call it like any native command.
The important detail, and the one that trips people up: the helm-secrets plugin does no cryptography itself. It delegates that to SOPS, the Secrets Operations editor originally built at Mozilla and donated to the CNCF (Cloud Native Computing Foundation) in 2023. SOPS encrypts and decrypts structured files in place, leaving the keys readable and encrypting only the values, so a diff on an encrypted values file still shows you which setting changed rather than one opaque blob.
SOPS supports PGP keys, age, AWS Key Management Service (KMS), GCP KMS, Azure Key Vault, HashiCorp Vault and OpenBao transit engines, and HuaweiCloud KMS as encryption keys. That choice matters more than the plugin itself, because it decides how your team shares access and how you rotate encryption keys later. For example, a KMS key per environment gives you revocation that a shared PGP keyring cannot. For a deeper walkthrough of each backend, see A Comprehensive Guide to SOPS.
Tutorial: Encrypt Helm chart values with SOPS and PGP
PGP is the oldest key store SOPS supports and the quickest way to see the workflow on one machine. For new team setups the SOPS maintainers recommend age instead, which the next subsection covers; the steps are identical, so start here.
Install SOPS. On macOS:
brew install sops
On Debian or Ubuntu, fetch the latest .deb from the SOPS releases page, which is v3.13.3 at the time of writing:
SOPS_VERSION=$(curl -s https://api.github.com/repos/getsops/sops/releases/latest | grep -o '"tag_name": *"[^"]*"' | cut -d'"' -f4)
curl -LO "https://github.com/getsops/sops/releases/download/${SOPS_VERSION}/sops_${SOPS_VERSION#v}_amd64.deb"
sudo dpkg -i "sops_${SOPS_VERSION#v}_amd64.deb"
sops --version
Next, install GnuPG and generate a key pair:
brew install gnupg
On Debian or Ubuntu, sudo apt-get install gnupg does the same job. Then create the key, putting your own name in KEY_NAME:
export KEY_NAME="Tiexin Guo"
export KEY_COMMENT="test key for sops"

gpg --batch --full-generate-key <<EOF
%no-protection
Key-Type: 1
Key-Length: 4096
Subkey-Type: 1
Subkey-Length: 4096
Expire-Date: 0
Name-Comment: ${KEY_COMMENT}
Name-Real: ${KEY_NAME}
EOF
Read the fingerprint back with gpg --list-keys:
$ gpg --list-keys
[keyboxd]
---------
pub   rsa4096 2026-09-27 [SCEAR]
      65E898A6DF79A111C62B7F459A815FE156C67FAC
uid           [ultimate] Tiexin Guo (test key for sops)
sub   rsa4096 2026-09-27 [SEA]
      50FADB58B9194C0444CE2C67FCFF6AFD55F5D6F9
The long hexadecimal string under pub is the fingerprint, which is how SOPS references PGP keys. gpg --list-secret-keys "${KEY_NAME}" prints it too.
Now configure SOPS to use that key. SOPS reads its configuration from a file named .sops.yaml, looking in the directory of the file it is encrypting and then in each parent directory, so one .sops.yaml at your chart repository root applies to every values file in the repo:
creation_rules:
    - pgp: >-
        65E898A6DF79A111C62B7F459A815FE156C67FAC
Substitute your own fingerprint, and that is the whole setup.
Now install the plugin. Pin the version rather than tracking latest, so your workstations and CI runners stay aligned:
helm plugin install https://github.com/jkroepke/helm-secrets --version v4.7.8
Confirm it registered:
$ helm plugin list
NAME    VERSION DESCRIPTION
secrets 4.7.8   This plugin provides secrets values encryption for Helm charts secure storing
Create a plaintext values file called credentials.yaml.dec:
password: test
Encrypt it with the following command:
helm secrets encrypt credentials.yaml.dec > credentials.yaml
Open credentials.yaml and you will see the key password in the clear with its value encrypted, plus the SOPS secret metadata block that records which key was used.
Reference the value from your chart's Secret template at your-chart/templates/secrets.yaml:
apiVersion: v1
kind: Secret
metadata:
  name: helloworld
  labels:
    app: helloworld
    chart: "{{ .Chart.Name }}-{{ .Chart.Version }}"
    release: "{{ .Release.Name }}"
    heritage: "{{ .Release.Service }}"
type: Opaque
data:
  password: {{ .Values.password | b64enc | quote }}
The labels here are ordinary application metadata, rendered by the Helm template like any other field. If you prefer to skip the base64 pipeline, swap data for stringData and Kubernetes encodes the value for you.
Install with helm secrets install instead of helm install. The plugin decrypts the values file on the fly:
helm secrets install release-name -f values.yaml -f credentials.yaml your-chart
Two rules to hold onto. Never commit credentials.yaml.dec, since it holds cleartext; add *.yaml.dec to .gitignore. The encrypted credentials.yaml is safe to commit as part of the chart.
There is also a trap in that .dec suffix worth knowing before it costs you an afternoon. If a decrypted credentials.yaml.dec is present and newer than credentials.yaml, the plugin uses the plaintext file instead of decrypting the encrypted one. That is a convenience for the edit loop, but it means a stale local file can silently override the values you committed, and a deploy that works on your laptop then fails in CI where the .dec file does not exist. Delete it once you have encrypted.
To share access across development teams, add their public key fingerprints to .sops.yaml and run sops updatekeys credentials.yaml to re-encrypt the file's data key against the updated recipient list. It rewrites only the metadata block, so the diff stays small, and it prompts for confirmation unless you pass -y. Access control lives in the SOPS configuration, not in the plugin, so onboarding someone is one commit rather than a new secret.
When someone leaves, the order matters. Remove their key from .sops.yaml first, run sops updatekeys so the data key is no longer encrypted to them, and only then run sops rotate -i to generate a fresh data key. Rotating first re-encrypts to every key still listed in the file, which at that point still includes theirs.
Tutorial: Switch SOPS from PGP keys to age encryption
PGP works, but managing keyrings, trust models, and key servers is a lot of overhead for encrypting a values file. The common modern alternative is age (always written lowercase), a small file encryption tool with a compact key format: no keyring, no key server, no expiration dates, and a key pair that fits in one text file. That makes it far easier to generate one of these encryption keys per environment and distribute the public half.
Install it. On macOS:
brew install age
On Debian or Ubuntu, sudo apt install age. Then generate a key pair:
mkdir -p ~/.config/sops/age
age-keygen -o ~/.config/sops/age/keys.txt
age-keygen prints the public key, which starts with age1, and writes both halves of the pair to keys.txt. Treat that file like an SSH private key: it is the only thing that decrypts.
The path matters, because SOPS looks for the private key in a default location when it decrypts. On Linux that is $XDG_CONFIG_HOME/sops/age/keys.txt, falling back to $HOME/.config/sops/age/keys.txt. On macOS the fallback is $HOME/Library/Application Support/sops/age/keys.txt, so if you followed the command above on a Mac, point SOPS at the file explicitly:
export SOPS_AGE_KEY_FILE=~/.config/sops/age/keys.txt
SOPS_AGE_KEY is the other override worth knowing, since it takes the private key content directly rather than a path. That is what the GitHub Actions example later in this guide uses, because a CI runner has no home directory worth writing to.
Now reference the public key in .sops.yaml. To let several people on the team decrypt the same values files, list their public keys separated by commas; each recipient's public key encrypts its own copy of the file's data key, and each person decrypts with their own private key:
creation_rules:
    - age: >-
        age12lycjufx6awzqv68439jm8hf24y6wz2nme3km465yrv6ga7ury8qmm09x8,
        age1qe5lxzzeppw5k79vxn3872272sgy224g2nzqlzy3uljs84say3yqgvd0sw
Everything else stays the same. helm secrets encrypt and helm secrets install behave identically, so migrating an existing chart means re-encrypting the values files against the new recipient and deleting the old PGP rule.
One caveat worth stating plainly, because plenty of blog posts overstate it: age encryption is simpler and has a much smaller implementation surface than PGP keys, but it is not stronger cryptography for this use case, and file encryption gives you no forward secrecy either way. Choose age because key management is easier, not because it makes an encrypted secret harder to crack.
Keep the private key out of the repository. Distribute it through your existing secret manager or your CI provider's encrypted storage, and back it up somewhere other than the laptop that generated it. SOPS has no recovery path: if the only key that can decrypt a values file is lost, that file is unreadable for good.
Tutorial: Pull values from a cloud secret manager with vals
The helm-secrets plugin has a second mode that stores nothing sensitive in the Helm chart at all. Instead of encrypted values, the Helm values file holds a reference, and the plugin resolves it at install time through vals.
Turn on the backend:
export HELM_SECRETS_BACKEND=vals
vals needs cloud provider credentials on whatever machine runs Helm, so make sure the caller can read from the secret store. Keep the same Secret template, this time with stringData so you can see the alternative:
apiVersion: v1
kind: Secret
metadata:
  name: helloworld
type: Opaque
stringData:
  password: '{{ .Values.password }}'
In values.yaml, replace the value with a reference:
password: ref+awssecrets://path/to/my/secret/value
On deploy, the plugin fetches that path from AWS Secrets Manager and injects it:
helm secrets install release-name -f values.yaml your-chart
The same syntax covers other providers, including Azure Key Vault, GCP Secret Manager, and HashiCorp Vault. For provider-specific paths, check the full documentation for vals.
Tutorial: Decrypt secrets in CI with GitHub Actions
Running helm secrets install from a laptop is straightforward. The harder problem is a pipeline, because your CI runner needs the decryption key without ever writing it to disk in a place that survives the job. GitHub Actions is where most teams hit this first.
With age encryption, this stays reasonably clean. Store the private key as a GitHub Actions repository secret named SOPS_AGE_KEY, then hand it to SOPS as an environment variable. Here is a working example of the workflow YAML file:
name: Deploy with helm-secrets
on:
  push:
    branches: [ main ]
jobs:
  deploy:
    runs-on: ubuntu-latest
    steps:
      - uses: actions/checkout@v7
      - name: Install SOPS and the helm-secrets plugin
        env:
          SOPS_VERSION: v3.13.3
        run: |
          curl -LO "https://github.com/getsops/sops/releases/download/${SOPS_VERSION}/sops_${SOPS_VERSION#v}_amd64.deb"
          sudo dpkg -i "sops_${SOPS_VERSION#v}_amd64.deb"
          helm plugin install https://github.com/jkroepke/helm-secrets --version v4.7.8
      - name: Deploy the chart
        env:
          SOPS_AGE_KEY: ${{ secrets.SOPS_AGE_KEY }}
        run: |
          helm secrets upgrade --install release-name \
            -f values.yaml -f credentials.yaml ./your-chart
Three things make this safe enough for production. The private key only exists as an environment variable inside one step, so it never lands in a file the next job can read. SOPS and the plugin are pinned, so a new release cannot change decryption behavior mid-pipeline. And the runner's own credentials, not a long-lived admin password, authenticate to the cluster.
If you use AWS KMS or GCP KMS instead of age, drop the key handling entirely and give the runner an OpenID Connect (OIDC) role with permission to decrypt with that specific key. That is the stronger pattern, because there is no private key to leak.
Troubleshooting common helm-secrets errors
Two failures account for most broken pipelines.
"no key found" during helm secrets install. The SOPS configuration does not match the key available to the caller, which usually means a values file for one environment is being decrypted with another environment's key. Split your creation rules by path so each environment resolves to its own key:
creation_rules:
  - path_regex: \.prod\.yaml$
    kms: 'arn:aws:kms:us-east-1:123456789:key/prod-key-id'
  - path_regex: \.dev\.yaml$
    kms: 'arn:aws:kms:us-east-1:123456789:key/dev-key-id'
Argo CD cannot decrypt values on sync. Argo CD needs both SOPS and the plugin present in the repo-server, and neither ships by default. Install them through an init container or a custom image, and pin the same versions you use locally. Version drift between your workstation and the repo-server produces decryption errors that look like key problems but are not.
What helm-secrets costs you in continuous deployment
If your team already uses SOPS, helm-secrets is a natural fit. The cost shows up in your CD system.
Integrating with Argo CD means the Argo CD repo-server needs SOPS and the plugin installed, which you achieve by building a custom Docker image or by installing them through an init container. I know that sounds like a lot of moving parts for one encrypted values file, because it is. Both options add maintenance: one more image to rebuild and patch, or a more complex values file for Argo CD itself.
So is there an easier way? That is exactly what the operator pattern is for, and it is the main reason teams running Helm deployments at scale end up there.
Option two: Sync secrets at deploy time with External Secrets Operator
The External Secrets Operator is a Kubernetes operator that reads from an external secret manager and writes the result into the cluster as a native Secret. It supports AWS Secrets Manager, HashiCorp Vault, Google Secret Manager, Azure Key Vault, and dozens of other backends. Our roundup of secrets management tools covers the wider landscape.
The difference from helm-secrets is where the reference lives. As shown in the previous section, helm-secrets keeps encrypted secrets or references in the Helm values file. External Secrets Operator keeps no Secret template in the Helm chart at all, and uses a custom resource called ExternalSecret instead.
How the External Secrets Operator works
Four moving parts:
- SecretStore: describes one secret manager and how to authenticate to it.
- ExternalSecret: maps specific remote keys to keys in a Kubernetes Secret it will create.
- Reconciliation: the operator watches ExternalSecret resources continuously.
- Refresh: it re-reads the remote value stored in the provider on the interval you set and updates the Secret when it changes.
API version note: the examples below use external-secrets.io/v1, which is the served version on the current release line. External Secrets Operator has moved to 2.x versioning, and 2.11 is current, so treat any tutorial still pinned to a 0.x chart as out of date. Older guides, including earlier versions of this article, use v1beta1. Version 0.16.2 was the last release to serve v1beta1, and 0.17.0 and later serve v1 only, so v1beta1 manifests fail on a current install. Note also that the project supports only the most recent minor version, so staying several releases behind means no security patches. If you run Argo CD or Flux against a recently upgraded operator, update the apiVersion in Git as well; the conversion webhook rewrites resources in-cluster and leaves GitOps reporting permanent drift otherwise.
Tutorial: Sync AWS Secrets Manager into a Helm chart
The idea here is simple: do not ship a Kubernetes Secret in the chart templates at all. Ship an ExternalSecret, which holds nothing but mappings.
Install the operator:
helm repo add external-secrets https://charts.external-secrets.io
helm repo update
helm install external-secrets \
  external-secrets/external-secrets \
  -n external-secrets \
  --create-namespace
The operator needs read access to AWS Secrets Manager. For a quick test, create a Secret holding an access key. Please do not do this in production:
echo -n 'KEYID' > ./access-key
echo -n 'SECRETKEY' > ./secret-access-key
kubectl create secret generic awssm-secret --from-file=./access-key --from-file=./secret-access-key
For real clusters, use Identity and Access Management (IAM) roles for service accounts and skip the static credentials entirely. See the AWS documentation and the External Secrets Operator documentation.
Create the SecretStore in secretstore.yaml, pointing at your account and region:
apiVersion: external-secrets.io/v1
kind: SecretStore
metadata:
  name: secretstore-sample
spec:
  provider:
    aws:
      service: SecretsManager
      region: ap-southeast-1
      auth:
        secretRef:
          accessKeyIDSecretRef:
            name: awssm-secret
            key: access-key
          secretAccessKeySecretRef:
            name: awssm-secret
            key: secret-access-key
Apply it:
kubectl apply -f secretstore.yaml
A SecretStore is namespaced, so it has to live in the same namespace as the ExternalSecret that references it. The manifest above sets no namespace and lands in whichever one your context points at, which is fine for a test as long as you install the chart there too. For a store that several namespaces share, use a ClusterSecretStore instead and set kind: ClusterSecretStore in the reference below.
Now add an ExternalSecret to your chart at your-chart/templates/externalsecret.yaml. This file contains only mappings, no sensitive data, so it is safe in any repository:
apiVersion: external-secrets.io/v1
kind: ExternalSecret
metadata:
  name: example
spec:
  refreshInterval: 1h
  secretStoreRef:
    name: secretstore-sample
    kind: SecretStore
  target:
    name: helloworld
    creationPolicy: Owner
  data:
  - secretKey: password
    remoteRef:
      key: MyTestSecret1
      property: password
That creates a Secret named helloworld with a password key, read from MyTestSecret1.password in AWS Secrets Manager. Install the chart normally, with no plugin and no decryption step:
helm install release-name -f values.yaml your-chart
Verify:
kubectl describe secret helloworld
From here, envFrom and secretRef in your Deployment consume the values as environment variables exactly as they would with a Secret template committed to the Helm chart.
Why External Secrets Operator fits CI/CD pipelines
helm-secrets needs tooling wherever Helm runs. External Secrets Operator needs nothing outside the cluster: no plugin, no SOPS binary, no local key material. It is installed once on the cluster side, which is the whole point of the operator pattern.
That makes CI/CD integration close to free. Argo CD, Flux, and GitHub Actions need no modification, because from their perspective the Helm chart contains ordinary manifests. The only change is on the chart side: ship an ExternalSecret instead of a Secret. Nothing is free, of course. The trade-off is a hard runtime dependency on the secret manager, and one more controller with broad read access for your security team to protect.
Option three: Commit encrypted manifests with Sealed Secrets
Sealed Secrets takes a third position. Like helm-secrets, the encrypted value lives in Git. Unlike helm-secrets, decryption happens only inside the target cluster, and nobody on the team ever holds the private key.
How the Sealed Secrets controller works
Two components:
- A controller in the cluster that generates a key pair on first start, keeps the private key as a Kubernetes Secret, and watches for SealedSecret custom resources.
- The kubeseal CLI, which encrypts a normal Secret manifest against the controller's public certificate.
Encryption is one-way and happens on your machine. A SealedSecret can be created by anyone with the public certificate, and decrypted only by the controller holding the matching private key. That is what makes the resulting file safe for version control, even in a public repository. Storing secrets this way keeps them secure without a secret manager in the loop.
One behavior surprises people: by default, kubeseal binds the encrypted value to a namespace and name. Move a sealed secret to another namespace and the controller refuses to unseal it. This is a deliberate guard against one team lifting another team's encrypted secret files, and it is configurable if you need it.
Tutorial: Seal a secret and ship it in a Helm chart
Install the controller with Helm:
helm repo add sealed-secrets https://bitnami-labs.github.io/sealed-secrets
helm repo update
helm install sealed-secrets sealed-secrets/sealed-secrets \
  --namespace kube-system
Install the CLI:
brew install kubeseal
Write a normal Secret manifest locally. This is the one file you never commit:
apiVersion: v1
kind: Secret
metadata:
  name: helloworld
  namespace: default
type: Opaque
stringData:
  password: test
Seal it. The --controller-name flag matters here, and leaving it off is the first thing that goes wrong for most people:
kubeseal --controller-name sealed-secrets --controller-namespace kube-system \
  -n default -f secret.yaml -o yaml > sealed-secret.yaml
kubeseal has to reach the controller to fetch its public certificate before it can encrypt anything, and it looks for a service called sealed-secrets-controller in kube-system by default. The Helm chart names the service after the release, so the install above produces sealed-secrets, and kubeseal fails with cannot fetch certificate: services "sealed-secrets-controller" not found. This mismatch between the chart and the CLI is long-standing and tracked upstream. Either pass --controller-name as shown, or install the chart with the release name sealed-secrets-controller so the defaults line up.
The output is a SealedSecret resource with the value encrypted. Drop it into your-chart/templates/sealedsecret.yaml, commit it, and install the Helm chart as usual. The controller unseals it in-cluster and produces a standard Secret named helloworld, which your Deployment consumes with no awareness that Sealed Secrets is involved.
Useful commands when a sealed secret does not unseal:
kubectl describe sealedsecret helloworld
kubectl logs -n kube-system deployment/sealed-secrets
kubeseal --fetch-cert --controller-name sealed-secrets --controller-namespace kube-system > cert.pem
Fetching the certificate to a file also lets developers seal secrets without cluster access: pass it with kubeseal --cert cert.pem and no controller connection is needed. That suits a workflow where only CI can talk to production.
Where Sealed Secrets falls short
It suits GitOps teams who want everything in Git and no runtime dependency on a secret manager. Three limits are worth knowing before you commit to it: two are security properties, and the third is an operational gap that tends to bite later.
The controller's sealing key is the entire trust boundary. Back it up or accept that a lost cluster means re-sealing every secret. Note that the controller renews its sealing key every 30 days by default and keeps the older keys so existing SealedSecrets still unseal, which means a backup taken once is not a backup of everything the cluster can currently decrypt; back up the sealing key Secret on a schedule, or set --key-renew-period=0 if you would rather manage renewal yourself.
Rotation is manual: changing a value means re-sealing the secret files and committing again, which is the same friction as SOPS. And there is no central inventory, so answering "where is this database credential used" means grepping Git repositories rather than querying a secret manager.
Option four: HashiCorp Vault Secrets Operator
If Vault is already your system of record, the Vault Secrets Operator is worth a look. It works much like External Secrets Operator: it watches Vault, writes values into Kubernetes Secrets, and keeps the destination in sync with the source over the lifetime of the resource.
The distinction is specialization. External Secrets Operator also supports Vault and works across every major cloud provider. Vault Secrets Operator works only with Vault, and in exchange supports Vault-specific capabilities such as dynamic secrets, where the operator requests short-lived database credentials on demand instead of syncing a static value.
Pick it if you are committed to Vault and want dynamic secrets. Pick External Secrets Operator if you have more than one backend now or expect to later.
How to restart pods automatically when secrets change
Rotating a credential is only half the job. The pod holding the old value keeps running until something restarts it, and none of the tools above do that on their own.
Without extra tooling, the common hack is a checksum annotation that changes whenever the Secret template changes, forcing a rolling update:
kind: Deployment
spec:
  template:
    metadata:
      annotations:
        checksum/config: {{ include (print $.Template.BasePath "/secrets.yaml") . | sha256sum }}
[...]
Plenty of teams run this in production and it does the job, but it has never looked to me like the simplest thing that could possibly work, and it only helps when the secret value lives in the chart. With helm-secrets you still need a full helm upgrade after every rotation, even when neither the app nor the chart changed, which is a lot of ceremony for one changed password. With External Secrets Operator it does not work at all: externalsecret.yaml holds only references, so the checksum never changes even though the underlying value did.
So none of the workarounds is satisfying. Reloader solves this properly. It watches Secrets and ConfigMaps and performs rolling upgrades on the workloads that consume them, including Deployments, DaemonSets, StatefulSets, and Rollouts.
Install it:
helm repo add stakater https://stakater.github.io/stakater-charts
helm repo update
helm install stakater/reloader --generate-name
Then annotate the Deployment in your chart template:
kind: Deployment
metadata:
  annotations:
    reloader.stakater.com/auto: "true"
spec:
  template:
    metadata:
[...]
Reloader discovers which ConfigMaps and Secrets that Deployment uses and restarts the pods when either changes. For example, a database password stored in AWS Secrets Manager and rotated on a 90-day schedule reaches the running pod without anyone touching the chart. Paired with External Secrets Operator, rotation in your secret manager propagates to running Helm deployments with no chart upgrade and no untidy checksum hack.
Why managing secrets in Helm is harder than it looks
Kubernetes is the common choice for running containerized workloads at scale, and Helm is the common way to ship applications onto a Kubernetes cluster. Deploying an app by hand means tracking a pile of manifests: Deployment, Service, ConfigMap, Secret, Ingress. Each one is a YAML file that has to stay in sync across environments, which is how teams end up with five near-identical copies of the same app and a copy-paste error in production.
Helm, the package manager for Kubernetes, solves that by bundling every manifest and dependency into a versioned chart you can install, upgrade, and share.
That is also where the problem starts. A Helm chart is designed to be shared and committed to version control. Secrets are designed to be neither. The moment a chart needs a database password or an API token, you have to answer two questions:
- Where does the sensitive data live? If the value sits in
values.yaml, it lands in Git the first time someone commits the chart. Hardcoded credentials in Git repositories are a large and growing source of secrets sprawl: GitGuardian detected 28.65 million new hardcoded secrets in public GitHub commits in 2025, a 34% increase year over year. - Who can read it? Charts get shared across teams and clusters. Access control has to travel with the chart, or the chart stops being safe to share.
This is not a theoretical security problem you can defer. Leaked credentials stay dangerous for years: of the credentials GitGuardian confirmed as valid in 2022, more than 64% were still valid when the same dataset was retested in January 2026, down only marginally from nearly 70% a year earlier. A password committed to a chart in a sprint you have forgotten is likely still a working key.
Kubernetes Secrets are encoded, not encrypted
Before comparing tools, it helps to be precise about what a Kubernetes Secret protects, because this one detail is what makes every option in this guide necessary. A Secret is a small object that holds sensitive data separately from your pod specs and ConfigMaps. The difference between a ConfigMap and a Secret is mostly intent and handling: ConfigMaps hold plain configuration, Secrets hold values Kubernetes treats as confidential, keeps out of pod definitions, and can encrypt at rest in etcd.
What a Secret does not do is encrypt anything on its own. The data field is base64, which is encoding, not encryption, so the object is a handling convention rather than a security control. Anyone with read access can view secrets in a cluster and decode them in one command:
kubectl get secret helloworld -o jsonpath='{.data.password}' | base64 -d
Two consequences follow. First, committing a rendered Secret manifest to Git is the same as committing the password. Second, you need to turn on encryption at rest for etcd and lock down role-based access control (RBAC), or every Secret stored in the cluster is readable by anyone who can list secrets.
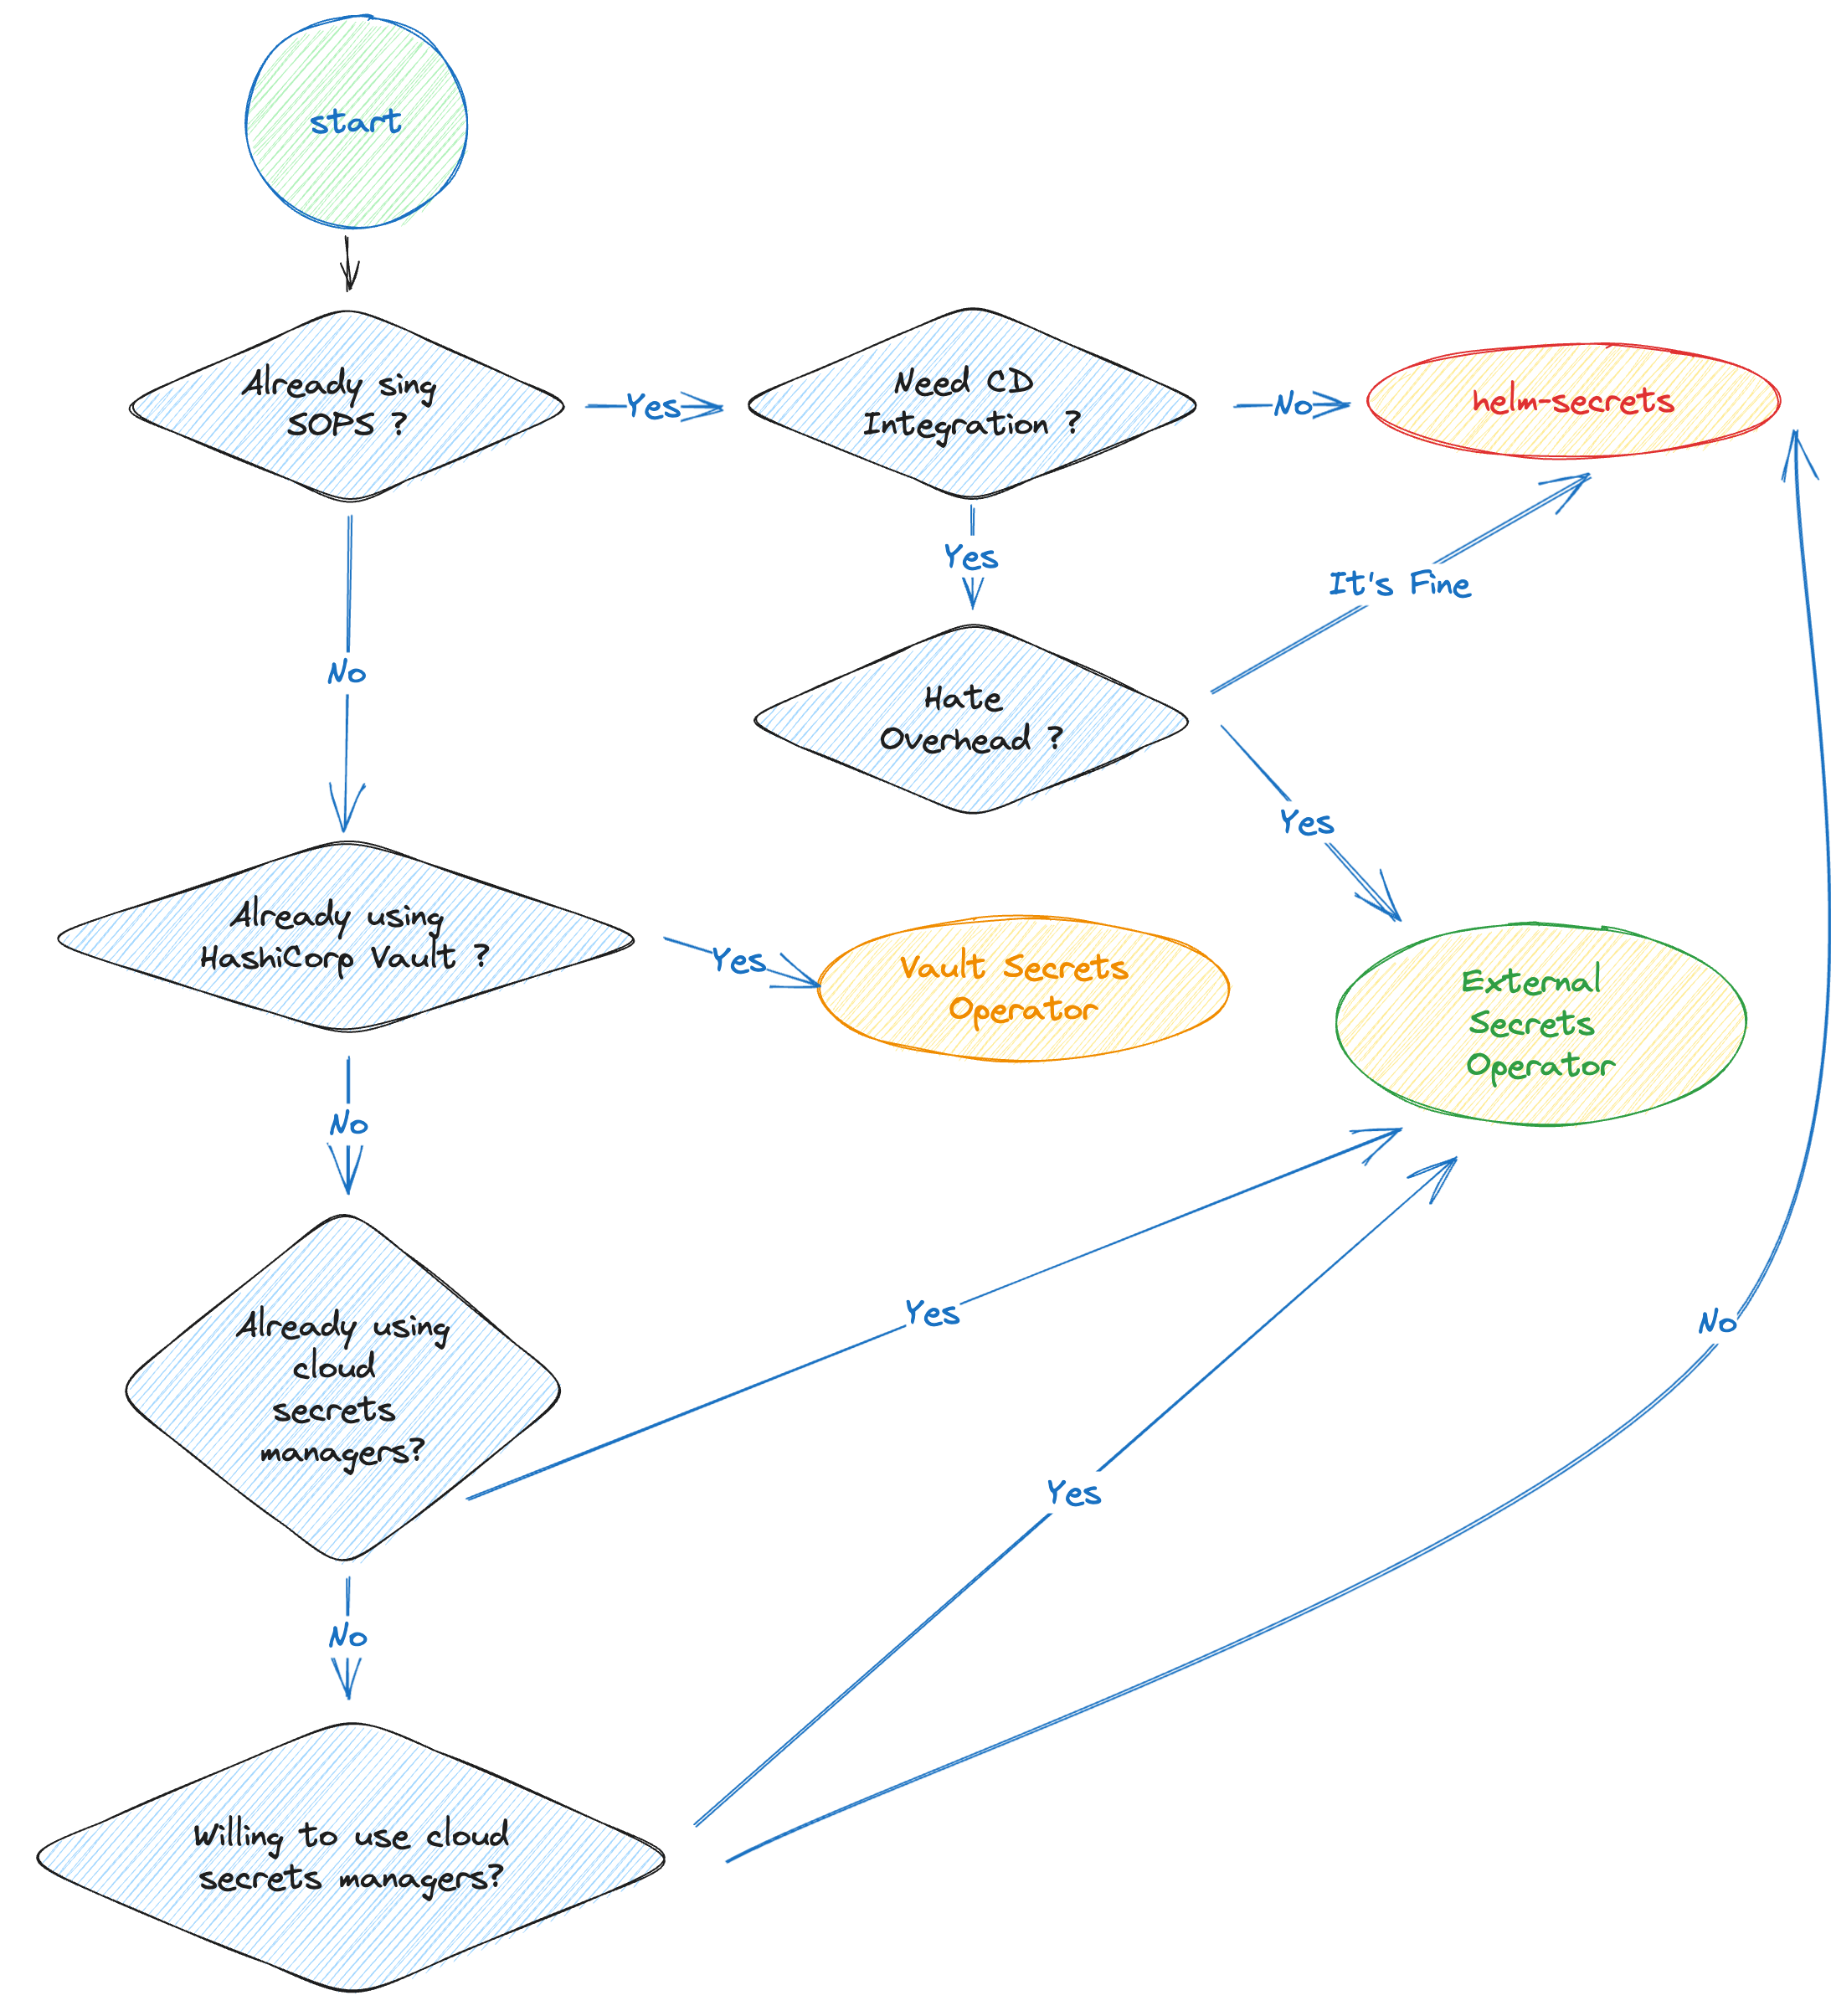
Which Helm secrets approach should you choose?
Your Helm secrets management choice comes down to what your team already runs, not to which tool is best in the abstract. The short version for managing secrets in a new chart:
- Small team, no secret manager, everything in Git: helm-secrets with SOPS and age.
- GitOps team that wants encrypted manifests in Git and no external dependency: Sealed Secrets.
- Any organization already running a secret manager: External Secrets Operator, plus Reloader for rotation.
- Committed to Vault and want dynamic secrets: Vault Secrets Operator.
Depending on your preferences and constraints, your mileage may differ. If you are inheriting a cluster rather than building one, External Secrets Operator is the one you are most likely to find already installed, and the one with the widest provider coverage if requirements change later.
Best practices for Helm secrets in production
Whichever tool you pick, the same operational rules apply. These best practices are what separate a working demo from secure deployments in production environments.
Grant least privilege on decryption. Only the identities that deploy should be able to decrypt secrets. For cloud KMS, attach a policy to the deploying role that allows decryption with one key and nothing else, rather than granting broad KMS access:
{
  "Version": "2012-10-17",
  "Statement": [
    {
      "Effect": "Allow",
      "Action": [
        "kms:Decrypt",
        "kms:DescribeKey"
      ],
      "Resource": "arn:aws:kms:region:account:key/key-id",
      "Condition": {
        "StringEquals": {
          "kms:EncryptionContext:AppName": "ExampleApp"
        }
      }
    }
  ]
}
Two things to note. This is an identity-based policy for the role that runs Helm, so it has no Principal block; if you are writing the key policy instead, add one. And the condition uses KMS encryption context, which is the mechanism that actually narrows a SOPS decrypt call: SOPS stores the context in the encrypted file's metadata, and KMS requires a matching context on every decrypt, so the role can only decrypt files created for that application. Set it when you create the file with sops --encryption-context AppName:ExampleApp values.prod.yaml. Resist the temptation to reach for the kms:ViaService condition here, which is a common mistake in copied policies: it restricts the key to calls arriving through a named AWS service, and SOPS calls KMS directly, so it would deny exactly the requests you are trying to allow.
Separate keys per environment. This is a cheap way to make a security incident survivable: one key per environment means a compromised development key cannot decrypt production values, and it makes the path-based SOPS rules above meaningful rather than cosmetic.
Turn on audit logging. Log every encryption and decryption call in KMS or Vault. Without it, your security team cannot answer who read which credential and when, which is the first question in any incident and a standing requirement in most compliance regimes.
Automate rotation. Long-lived credentials are the root problem, not the storage format. Pair a rotation schedule in your secret manager with Reloader so rotation does not require a human running helm upgrade.
Scan charts before they reach Git. Every approach here fails the same way: someone tests locally with a plaintext value, forgets the .dec suffix, and commits it. Encryption at rest does nothing about a secret that was never encrypted. A pre-commit hook or CI check that scans Helm charts, values files, and the output of helm template catches that class of mistake, which is why mature secrets management programs run secrets detection alongside SOPS or an operator rather than instead of it. GitGuardian's ggshield does this as a pre-commit hook or CI step, and covers the case none of these tools can: a credential that reached the repository unencrypted.
Do not treat base64 as a control. Worth repeating because it still shows up in security review: a Secret manifest with a base64 value is a plaintext credential in a costume.
FAQ
What are the main approaches to managing secrets in Helm charts?
There are two. You either store encrypted secrets inside the Helm chart, using the helm-secrets plugin with SOPS or Sealed Secrets with kubeseal, or you keep secret values out of the chart entirely and sync them at deploy time with External Secrets Operator or Vault Secrets Operator. The first keeps charts self-contained but makes you own key management. The second removes secrets from Git but adds a runtime dependency on wherever the value is stored, so the secure choice depends on whether you already run a secret manager.
How does the helm-secrets plugin integrate with SOPS and cloud secret managers?
The helm-secrets plugin does no cryptography itself. It calls SOPS to encrypt and decrypt values files, and helm secrets install decrypts on the fly at deploy time. Setting HELM_SECRETS_BACKEND=vals switches it to reference mode, where a value like ref+awssecrets://path/to/secret is resolved from AWS Secrets Manager, Azure Key Vault, or HashiCorp Vault during the Helm operation.
Should I use age encryption or PGP keys with SOPS for Helm secrets?
Use age encryption for new setups. It uses short public and private key pairs with no trust model or key servers, so generating a key per environment and distributing the public half is far simpler than the equivalent GnuPG workflow. Both are strong enough for encrypting a values file, and neither provides forward secrecy for files at rest, so pick age for operational simplicity rather than cryptographic strength.
Why do my helm-secrets deployments fail in CI/CD pipelines?
Almost always a key or version problem. "No key found" means the values file being decrypted does not match the key available to the runner, which path-based creation_rules in .sops.yaml fix. On Argo CD, the repo-server needs SOPS and the plugin installed through an init container or custom image, pinned to the same versions used locally, since version drift produces decryption errors that look like key errors.
How can I make Kubernetes pods restart automatically when secrets are updated?
Install Reloader and add the reloader.stakater.com/auto: "true" annotation to your Deployment. Reloader watches the Secrets and ConfigMaps a workload consumes and performs a rolling restart when either changes. The sha256sum checksum annotation is the alternative, but it only works when the value lives in the chart, so it does nothing for External Secrets Operator.
What is the difference between Kubernetes ConfigMaps and Secrets?
ConfigMaps hold non-sensitive configuration; Secrets hold values Kubernetes treats as confidential, keeps out of pod specifications, and can encrypt at rest in etcd. The important caveat is that a Secret's data field is base64 encoded, not encrypted, so anyone able to read secrets in the cluster can decode them with kubectl get secret <name> -o jsonpath='{.data.key}' | base64 -d.
Should I use External Secrets Operator or helm-secrets for multi-cloud environments?
External Secrets Operator, in most cases. For multi-cloud secrets management it supports many providers behind one interface, needs nothing installed where Helm runs, and requires no changes to Argo CD or Flux. helm-secrets suits file-based or single-backend workflows, but every machine and runner that deploys needs SOPS, the plugin, and access to the right key.
Is Helm still the right choice for Kubernetes deployments?
Yes for packaging and distributing applications, which is what it does well. Kustomize is the common alternative and takes an overlay-based approach with no templating, which some teams prefer for readability. Neither solves secrets on its own, so whichever you choose, the security options in this guide still apply. For example, External Secrets Operator works the same way under Kustomize as it does under Helm.
This article is a guest post. Views and opinions expressed in this publication are solely those of the author and do not reflect the official policy, position, or views of GitGuardian. The content is provided for informational purposes; GitGuardian assumes no responsibility for any errors, omissions, or outcomes resulting from the use of this information. Should you have any inquiries with regard to the content, please contact the author directly.
 Tiexin Guo
 Tiexin Guo