SOPS Guide: How to Encrypt and Manage Secrets in Git, Kubernetes, and CI/CD
Pasted a secret into a chat window and promised to clean it up later? Here's how SOPS works with age, AWS KMS, and HashiCorp Vault.
Pasted a secret into a chat window and promised to clean it up later? Here's how SOPS works with age, AWS KMS, and HashiCorp Vault.
Learn how to automate Helm deployments with GitOps, using Argo CD for continuous delivery. Seamlessly handle secrets, pod auto-restart, and version propagation in Kubernetes with this production-ready integration.
Learn step-by-step techniques and best practices to handle secrets in Helm charts safely and effectively. Level up your Helm deployments today!
Learn the best practices for handling secrets in Go in the cloud-native ecosystem.
In this article we present a novel way to protect your container applications post-exploitation. This additional protection is called Seccomp-BPF.
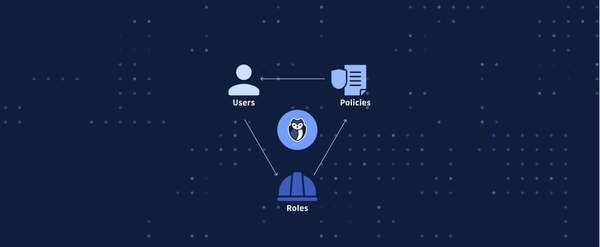
Get started with IAM by using Terraform to create users, groups, and policies.
When building an application that requires user authentication, implementing a secure login flow is critical. In this article, we'll walk through how we created a robust OAuth login flow for ggshield, our Python-based command line tool, to streamline the onboarding process for our users.
In this guide, we'll walk you through integrating CyberArk Conjur with GitGuardian, step by step.
Tiexin Guo Senior DevOps Consultant, Amazon Web Services Author | 4th Coffee In the cloud-native era, Infrastructure as Code (IaC; read more about it in this blog here) has become the de-facto standard for managing cloud infrastructure, and more. While Terraform has been
Join Mackenzie Jackson and Sonya Moisset for an eye-opening discussion about Ethical Hacking as Sonya answers questions from Mack and the webinar audience.
Enjoy highlights from GitGuardian's ethical hacking webinar with a friend from Snyk.
A condensed recap of our hands-on runtime security webinar from September. Get the juiciest knowledge nuggets and pointers to more.

GitGuardian is the code security platform for
the DevOps generation.
With automated secrets detection and
remediation, our platform enables Dev, Sec, and Ops to advance together
towards the Secure Software Development Lifecycle.
Subscribe to our newsletter to receive the latest content and updates from GitGuardian.