Secrets detection
Why We Built the Good Samaritan Program
The first thing GitGuardian ever shipped was a free warning. Now we’re making sure it gets heard.
The first thing GitGuardian ever shipped was a free warning. Now we’re making sure it gets heard.
The first thing GitGuardian ever shipped was a free warning. Now we’re making sure it gets heard.
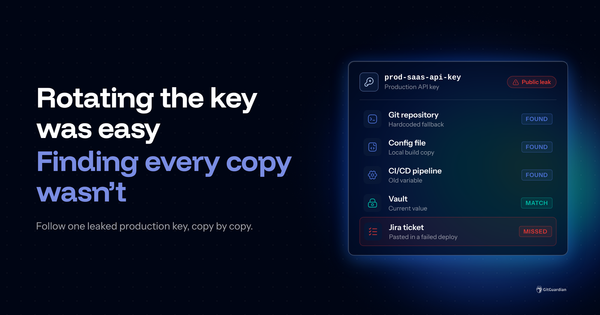
A leaked production key had copies in code, config, a pipeline, a vault and Jira. Follow the credential rotation twice, once by hand over 3 days and once with a full inventory in hours.
During a six-month internship with the GitGuardian security research team, Florent Leroy built the attribution rules and live checkers described in this post. Since Aug. 5, they run in production.
A threat actor used stolen GitHub credentials to push a CI secret stealer into more than 17,000 public repositories. GitHub held the malicious workflows. An npm hook got past the hold and ran. Here is how the bypass worked and what to rotate if you were hit.
AI coding agents can read files, call tools, and use credentials that never appear in a pull request. For AppSec teams, securing the code is only part of the job.
Learn how AntiFox and ARTEX use agentic AI to find and exploit exposed credentials, what AWS intrusions reveal, and how security teams can reduce credential exposure.
An ARTEX build ships no secret scanner. In our lab, it found 8 of 9 planted secrets in seconds, even when asked only to assess the repo.
~45 agentic attack frameworks beyond ARTEX, fingerprinted for internet scanning: dozens of operator consoles sit exposed today, many unauthenticated.
31,088 secrets in Claude Code’s .claude/settings.local.json on public GitHub, 5,343 valid at detection, 23,276 repositories. 613 more in Docker Hub images, 99 valid. Validity, timeline, Docker Hub, who is affected.
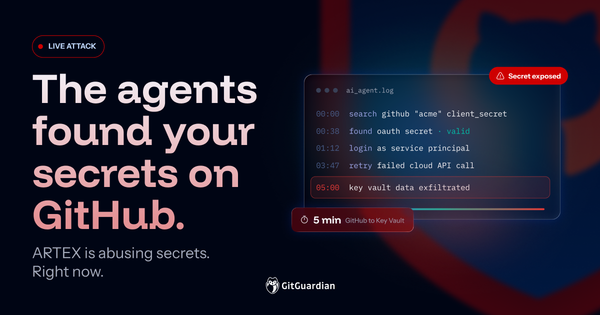
Microsoft Threat Intelligence caught attackers using an agentic AI framework, ARTEX, to hunt exposed secrets on public GitHub and move into Azure tenants in as little as five minutes. GitGuardian has tracked this attack path since 2017. Here is what changed, and four things to do today.
Kubernetes Secrets are base64 encoded, not encrypted, so a password in values.yaml is a working credential in Git. Compare four ways to keep secrets out of your Helm charts and find the one that fits what your team already runs.
The initial access vector changes, but the path stays the same: stolen credentials. Lessons from Binance and other recent crypto compromises.

GitGuardian is the code security platform for
the DevOps generation.
With automated secrets detection and
remediation, our platform enables Dev, Sec, and Ops to advance together
towards the Secure Software Development Lifecycle.
Subscribe to our newsletter to receive the latest content and updates from GitGuardian.