Scanning GitHub Gists for Secrets with Bring Your Own Source
Developers treat GitHub Gists as a "paste everything" service, accidentally exposing secrets like API keys and tokens. BYOS lets you scan and monitor these blind spots.
Developers treat GitHub Gists as a "paste everything" service, accidentally exposing secrets like API keys and tokens. BYOS lets you scan and monitor these blind spots.
Ever accidentally pasted an API key into a web form? Chromegg is our new Chrome extension that scans form fields in real-time, alerting you BEFORE you submit secrets. Open-source & ready to use!
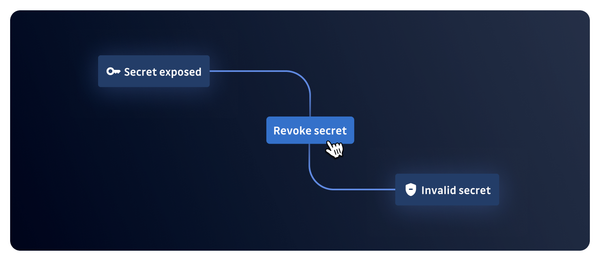
Secure your secrets with GitGuardian's new one-click revocation. Instantly neutralize exposed secrets to close the attack window and automate your incident response.
Discover how to automatically detect secrets in GitLab CI logs using ggshield and GitGuardian's Bring Your Own Source initiative. Learn to set up real-time scanning to prevent credential leaks, enhance compliance, and secure your entire CI/CD pipeline from hidden risks.
Discover what generic secrets detection is really about, why it's a critical component to build a performant secrets detection engine, and how GitGuardian is tackling this problem.
Learn how GitGuardian and Delinea solve the growing problem of improper offboarding for Non-Human Identities (NHIs). Discover why orphaned secrets are a top security risk and how to automate their lifecycle management.
Discover how GitGuardian's "Bring Your Own Source" initiative enables security teams to extend secrets detection beyond code repositories, leveraging custom integrations to eliminate a significant hidden attack surface.

GitHub's Push Protection is now enabled by default for all public repositories, a big milestone for open-source security! Find out the key points you need to keep in mind before using it to safeguard your code repositories.
Our latest State of Secrets Sprawl 2025 research reveals a troubling reality: the majority of leaked corporate secrets found in public code repositories continue to provide access to systems for years after their discovery.
Private repos leak plaintext secrets 8x more often than public ones. Learn why internal codebases are the biggest blind spot in your secrets management strategy.
AI adoption accelerates secret sprawl as organizations connect to multiple providers. Our investigation of a leaked xAI API key, which granted access to unreleased Grok models, reveals critical flaws in their disclosure process, highlighting necessary improvements in this domain.

GitGuardian is the code security platform for
the DevOps generation.
With automated secrets detection and
remediation, our platform enables Dev, Sec, and Ops to advance together
towards the Secure Software Development Lifecycle.
Subscribe to our newsletter to receive the latest content and updates from GitGuardian.