Secrets Management

A collection of 37 posts

React2STEAL: Hijacked GitHub Accounts Exploit React2Shell and Publish Stolen Secrets

React2STEAL: Hijacked GitHub Accounts Exploit React2Shell and Publish Stolen Secrets

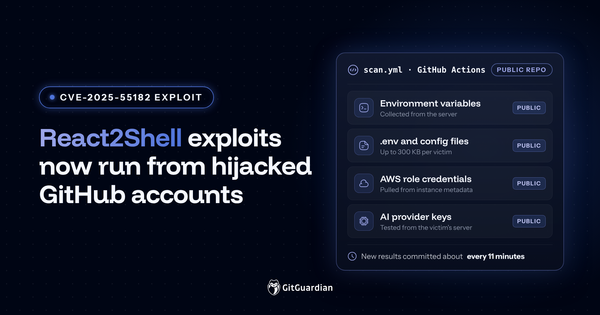
React2STEAL uses GitHub Actions in hijacked accounts to exploit React2Shell (CVE-2025-55182) on Next.js servers, then commits stolen environment variables, cloud keys, and AI API keys to public repositories. Patch, then revoke every secret the server could reach.
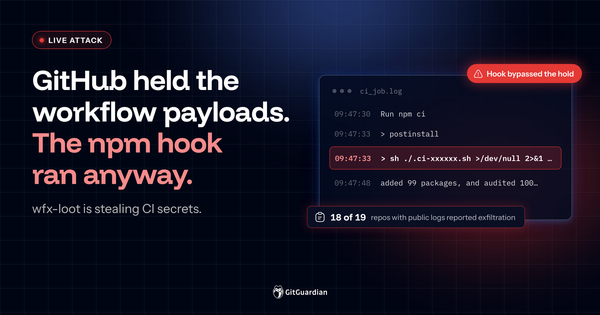
wfx-loot: A CI Secret Stealer Pushed With Stolen GitHub Credentials

wfx-loot: A CI Secret Stealer Pushed With Stolen GitHub Credentials

A threat actor used stolen GitHub credentials to push a CI secret stealer into more than 17,000 public repositories. GitHub held the malicious workflows. An npm hook got past the hold and ran. Here is how the bypass worked and what to rotate if you were hit.

The Agents Have Now Found Your Secrets On GitHub: ARTEX Is Abusing Public Secrets Right Now

The Agents Have Now Found Your Secrets On GitHub: ARTEX Is Abusing Public Secrets Right Now

Microsoft Threat Intelligence caught attackers using an agentic AI framework, ARTEX, to hunt exposed secrets on public GitHub and move into Azure tenants in as little as five minutes. GitGuardian has tracked this attack path since 2017. Here is what changed, and four things to do today.

How to Handle Secrets in Helm

How to Handle Secrets in Helm

Kubernetes Secrets are base64 encoded, not encrypted, so a password in values.yaml is a working credential in Git. Compare four ways to keep secrets out of your Helm charts and find the one that fits what your team already runs.

How GitGuardian Secures the Credential Layer: From Discovery to Remediation

How GitGuardian Secures the Credential Layer: From Discovery to Remediation

Credential layer security is more than detection. Follow one credential through the GitGuardian platform, from discovery across repos, CI/CD, laptops, and vaults to owner and access context, safe remediation, and prevention.

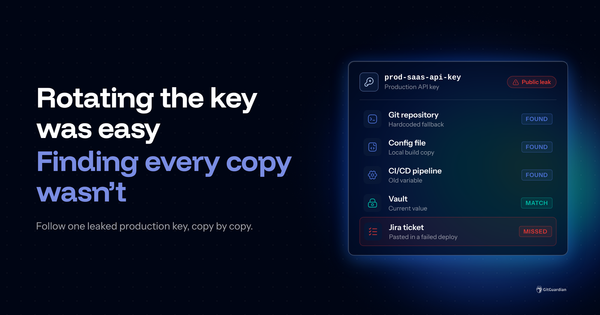
Rotating 1,000 Service Account Passwords With Zero Outages: Why the Inventory Comes First

Rotating 1,000 Service Account Passwords With Zero Outages: Why the Inventory Comes First

Rotating 1,000+ service credentials across 150+ applications with zero outages took one lesson: rotation is the last step. Here’s the six-stage SCALER method, from inventory to rotation, and why a revert path made it safer.

OWASP Top 10 Kubernetes Security Risks Explained: Why Credentials Deserve a Closer Look

OWASP Top 10 Kubernetes Security Risks Explained: Why Credentials Deserve a Closer Look

GitGuardian researchers reached 44 active Kubernetes clusters through leaked secrets, and 30% had been exposed for more than two years. Here’s how the OWASP Kubernetes Top 10 explains these Kubernetes security risks, and why K03, Secrets Management Failures, turns one leak into a chain.