Breach explained
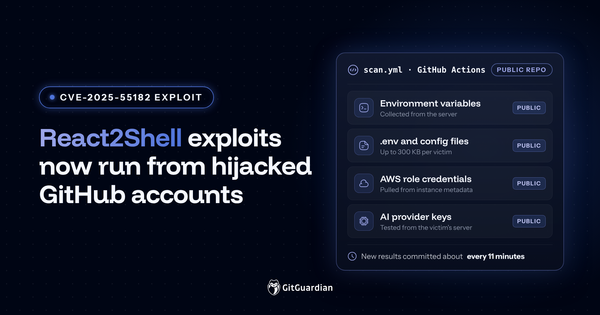
React2STEAL: Hijacked GitHub Accounts Exploit React2Shell and Publish Stolen Secrets
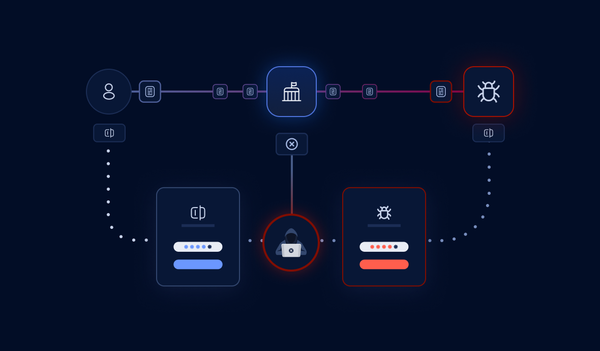
React2STEAL uses GitHub Actions in hijacked accounts to exploit React2Shell (CVE-2025-55182) on Next.js servers, then commits stolen environment variables, cloud keys, and AI API keys to public repositories. Patch, then revoke every secret the server could reach.