CloudNativeSecurityCon 2023: A Unique Community Event Focused On The Future Of Open Source and Cloud Native Security
Read some of the highlights from CloudNativeSecurityCon 2023, the first-of-its-kind in-person event, grown from the conversations of the community on the front lines of open source security.

GitGuardian Named Leader in G2 and Sourceforge Winter 2023 Reports
GitGuardian has been awarded four new badges in G2’s Winter 2023 Report and has been named a leader by Sourceforge.
Supply Chain Security: What is SLSA? (Part I)
Attacks on software supply chains have been around for some time, but recently they have evolved into much more dangerous threats. Let's dive into the SLSA framework to understand where supply chain security is headed.
Using GGCanary to Create Your Own Honeytokens with Open Source Tools - Complete Tutorial
Honeytokens or Canary Tokens are credentials designed to alert you when an attacker is in your infrastructure. This is a complete tutorial how to create them using only open-source projects.

Q4 2022 Product Roundup – find and fix hardcoded secrets
Learn more about the challenges awaiting organizations of hundreds to thousands of developers deploying secrets detection and how we're addressing them with our latest feature releases.

IAM Best Practices [cheat sheet included]
Download our cheat sheet on IAM, Identity and Access Management, best practices. It will help you make your cloud environments more secure.
How to Handle Secrets in Python
DevOps engineers must handle secrets with care. In this series, we summarize best practices for leveraging secrets with your everyday tools.

Azure repos native integration with GitGuardian
DevOps teams and developers can now bring the power of automated secrets detection and remediation to their Azure DevOps repositories.
Top 10 Practices for Secure Software Development
Developer security practices are about adding security at each software development stage. Here’s a list of top developer security practices to follow.

10 Tips to Optimize PostgreSQL Queries in Your Django Project
Philippe is back, this time joined by Laurent, to reveal their best tips & tricks to make Django and Postgres the best friends in the world.

How To Secure Your CI/CD Pipeline
After CircleCI breach, it is a good moment for any team relying on CI/CD infrastructure to review their pipeline security as there are some steps they can take to be proactive.
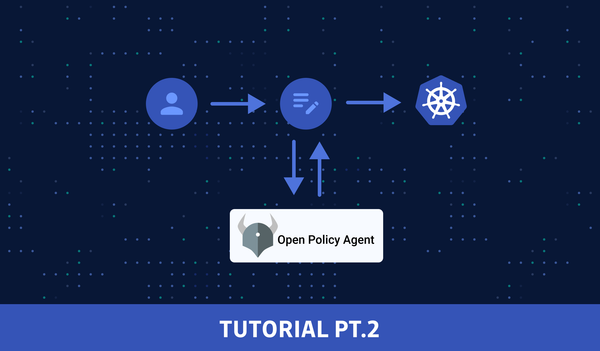
Open Policy Agent with Kubernetes - Tutorial (Pt. 2)
This time, we will see how to get a deeper integration between OPA and Kubernetes with Gatekeeper and native CRD-based policies.